Claude Code Extension Backdoor (2.1.313): What Happened & How to Check
A tampered Claude Code extension 2.1.313 in Cursor's marketplace planted an SSH backdoor on up to 5,000 machines. Affected versions, how to check for svc-telemetry, and fixes.
Quick answers
- What was the Claude Code extension backdoor?
- On Oct 29, 2026, a tampered Claude Code extension, anthropic.claude-code 2.1.313, was served in Cursor's extension marketplace. It tried to plant a persistent SSH backdoor. Anthropic did not build it.
- Which version is affected?
- Version 2.1.313 installed from the Cursor Marketplace between about 2:27am and 1:35pm PT on Oct 29, 2026. Microsoft also lists 2.1.312 from the same marketplace. The clean version is 2.1.314.
- Am I affected if I use VS Code or the npm CLI?
- Microsoft says the bad packages were never on the Visual Studio Marketplace or npm. All evidence points to Cursor's marketplace only.
- How do I check my machine?
- Search ~/.ssh/authorized_keys for "svc-telemetry". If it's there, you're hit: isolate the machine, run Cursor's cleanup script and rotate credentials.
If Cursor auto-updated your Claude Code extension on October 29, check your SSH keys now. It takes 10 seconds.
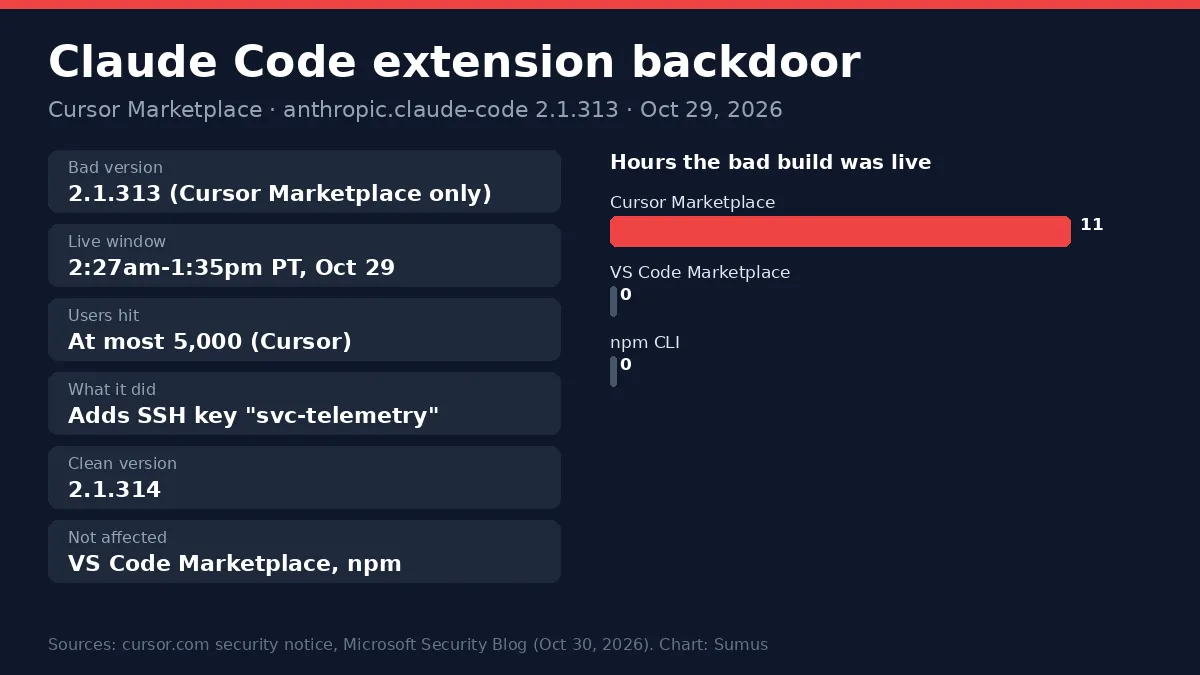
Cursor confirmed that a "maliciously modified version of Anthropic's Claude Code extension" was live in its VS Code extension marketplace for about 11 hours. The build, 2.1.313, tried to add an attacker's SSH key, open a reverse SSH tunnel and survive reboots. Cursor says at most 5,000 users got it.
1. Claude Code extension backdoor at a glance
Item | Detail |
|---|---|
Package | anthropic.claude-code 2.1.313 (Microsoft also lists 2.1.312) |
Where | Cursor VS Code extension marketplace only |
When | ~2:27am-1:35pm PT, Oct 29, 2026 |
Users affected | At most 5,000 (Cursor) |
Built by Anthropic? | No |
Payload | 66-line loader added to extension.js |
Marker | SSH key labeled svc-telemetry |
Attacker server | 134.209.82.225, now offline |
Clean version | 2.1.314 |
2. What happened
Researchers at Phorion and OpenSourceMalware spotted the bad build. A 66-line loader sat at the top of extension.js, in front of the normal extension code, so the extension still looked and worked like Claude Code. It ran when the editor started, with no click needed.
- It collected host details: hostname, username, OS, home folder, Git email, public IP and the names of environment variables.
- It added an attacker SSH key, labeled svc-telemetry, to authorized_keys.
- It tried to turn on the local SSH server and open a reverse tunnel to 134.209.82.225.
- It set up persistence: a LaunchAgent on macOS (com.apple.sysmond), a SysMon scheduled task or Startup script on Windows, cron @reboot on Linux.
- It reported back over HTTP to port 8099.
Cursor says that turning on SSH needs admin rights, so on most Macs and Windows PCs the tunnel step failed. But the key and persistence still got installed, so clean up anyway.
3. Official statements
- Cursor: the malicious version "was not developed by Anthropic." Cursor pulled it, shut down and rebuilt its marketplace, rotated keys, audited other extensions and had the attacker server taken offline.
- Microsoft: the bad packages "were never published nor distributed" from the Visual Studio Marketplace or npm. "Anthropic confirmed to Microsoft that their systems were not compromised."
- Anthropic: shipped 2.1.314. As of Oct 30, Ars Technica reported no public notice from Anthropic yet, and how the attacker got into the Cursor listing is still not public.
4. How to check if you're affected
You're at risk only if you installed or auto-updated Claude Code from the Cursor marketplace during the window. Run Cursor's check:
- macOS / Linux: `grep -qs svc-telemetry ~/.ssh/authorized_keys && echo "found" || echo "not found"`
- Windows (PowerShell): search `$HOME\.ssh\authorized_keys` and `C:\ProgramData\ssh\administrators_authorized_keys` for svc-telemetry.
- Also look for `~/.config/.smt`, `~/.config/.smtk`, a `.stk_` temp file, and the persistence items above.
- Check extension version: anything other than 2.1.313/2.1.312 from Cursor's marketplace was not part of this incident.
5. How to fix it
- Isolate the machine if the key is there.
- Run Cursor's remediation script (remediate-macos.sh as your user, or remediate-windows.ps1 as admin) from the security notice. Uninstalling the extension is not enough; the persistence scripts keep running.
- Update Claude Code to 2.1.314 or later.
- Rotate every secret the machine could reach: cloud keys, GitHub tokens, API keys, SSH keys, sessions. Do it from a clean device.
- Consider rebuilding the machine if the payload ran.
6. Don't put all your AI work in one tool
Yes, you can keep working while you clean up. In Sumus, Claude, GPT, Gemini and other top models work side by side as AI employees in one team chat, in the cloud. If one tool or extension goes down, switch the model, not your whole workflow, and keep your team's work in one thread.
What we're watching
- A public post-mortem from Anthropic or Cursor on how the listing was taken over.
- Any sign that credentials were used through the backdoor.
- Changes to extension signing on Open VSX and Cursor.
FAQ
Was the official Claude Code extension hacked?
The copy served in Cursor's marketplace under Anthropic's listing was tampered with. Anthropic says its own systems were not compromised, and the VS Code Marketplace and npm builds were clean.
What is svc-telemetry?
The label on the attacker's SSH key that the bad extension added to ~/.ssh/authorized_keys. Finding it means your machine was hit.
Is Claude Code safe to use now?
Cursor removed the bad version and says it has no evidence other versions are affected. Update to 2.1.314 or later and check for svc-telemetry.
Does uninstalling the extension remove the backdoor?
No. The payload installs separate persistence scripts. Run Cursor's remediation script and rotate credentials.
Can I use Claude without an editor extension?
Yes. Sumus lets your team use Claude and other top models as AI employees in a cloud group chat.
Sources
- Cursor, Security notice: malicious Anthropic.claude-code 2.1.313, Oct 29, 2026.
- Microsoft Security Blog, Inside a malicious Claude Code-branded extension, Oct 30, 2026.
- OpenSourceMalware and Phorion advisories, Oct 30, 2026.
- Ars Technica and The Hacker News, Oct 30, 2026.
Update log
- — Oct 31: First published. Claude Code extension 2.1.313 backdoor in Cursor's marketplace: what happened, check and fix.